← Open Source
netbirdio

netbird

NetBird securely connects people, machines and AI agents across any network with one identity-based Zero Trust platform. Powered by peer-to-peer WireGuard®.

InfrastructureMake world agent-readyGo
Open on GitHub
Momentum
+34stars in 24 hours+0.1%
30.0k
Stars
1.76k
Forks
100
Contributors
Created 2021-04-14 · Updated 2026-10-16 · #512 today
Top developers

netbirdio/netbird is ranked 512 with 30,012 stars.

Same-category comparison

netbirdio/netbird is ranked 512 among these 8 peers; FlashML-org/FreeVideo is ranked 503.

Same-category comparison
NameRankMetrics
ml-explore/mlx-lm459
Language:
Python
Stars:
7,350
Forks:
1,129
Description:
Run LLMs with MLX.
mw00/project-maya490
Language:
C++
Stars:
928
Forks:
115
Description:
Project Maya - run GLM-5.3-Flash (321B MoE) privately on your own GPU(s), from one card to 16, NVIDIA or AMD, Linux or Windows. Engine, server, dashboard, OpenAI- and Anthropic-compatible API, quant tools.
facebookincubator/muse-gadget-sdk502
Language:
C
Stars:
2,222
Forks:
466
Description:
Open source SDK to build Muse gadgets.
FlashML-org/FreeVideo503
Language:
Python
Stars:
1,993
Forks:
209
Description:
Make videos on the computer you already own. FreeVideo runs MiniMax H3 in as little as 8 GB of VRAM and 16 GB of RAM, and adapts its acceleration path to your hardware.
jundot/omlx524
Language:
Python
Stars:
22,861
Forks:
2,056
CopilotKit/OpenBot562
Language:
TypeScript
Stars:
6,537
Forks:
902
Description:
Open-source AI coworkers that each get a computer of their own: a browser, files and tools, with every action decided before it happens and recorded after. Bring any AG-UI agent.
microsoft/mxc564
Language:
Rust
Stars:
2,859
Forks:
153
Description:
Policy-driven, layered isolation and containment.
ovg-project/kvcached578
Language:
Python
Stars:
1,728
Forks:
208
Description:
Virtualized Elastic KV Cache for Dynamic GPU Sharing and Beyond.
Key parameters and specifications
ParameterValue
LanguageGo
CategoryInfrastructure
SubcategoryMake world agent-ready
KeywordsClient integration, DevOps, IoT, Security
Stars30,012
Forks1,760
Contributors100
Created date2021-04-14
Updated date2026-10-16
Stars in 1 day34
Rank512
Previous rank560
Rank change48
7-day stars rank19,063
Previous 7-day stars rank18,978
7-day stars rank change-85
Total stars rank435
Previous total stars rank435
Total stars rank change0
README summary

**NetBird combines a configuration-free peer-to-peer private network and a centralized access control system in a single platform, making it easy to create secure private networks for your organization or home. ** NetBird creates a WireGuard-based overlay network that automatically connects your machines over an encrypted tunnel, leaving behind the hassle of opening ports, complex firewall rules, VPN gateways, and so forth. ** NetBird enables secure remote access by applying granular access policies while allowing you to manage them

intuitively from a single place. Works universally on any infrastructure. Quickstart with self-hosted NetBird This is the quickest way to try self-hosted NetBird. It should take around 5 minutes to get started if you already have a public domain and a VM. Follow the Advanced guide with a custom identity provider for installations with different IdPs. **Infrastructure requirements:** A Linux VM with at least **1 CPU** and **2 GB** of memory. The VM should be publicly accessible on

TCP ports **80** and **443** and UDP port **3478**. A **public domain** name pointing to the VM. **Software requirements:** Docker with the Compose plugin (Compose v2 or higher). **Steps** Download and run the installation script: A bit on NetBird internals Every machine in the network runs the NetBird agent, which manages WireGuard. Every agent connects to the Management Service, which holds network state, manages peer IPs, and distributes updates to agents. Agents use ICE (via pion/ice) to discover connection

candidates for peer-to-peer connections. Candidates are discovered with the help of STUN servers. Agents negotiate a connection through the Signal Service, exchanging end-to-end encrypted messages with candidates. mobile carrier-grade NAT) and a direct p2p connection isn't possible, the system falls back to a Relay Service and a secure WireGuard tunnel is established through it. See a complete architecture overview for details. Reporting bugs and requesting features NetBird uses a discussion-first workflow. Bug reports and

feature requests start in Discussions, not as issues. Validated reports are promoted to issues. This keeps the issue tracker a clear answer to one question: what is the team working on. Please search existing discussions and issues first, including closed ones. If something similar already exists, upvote it and add your details there instead of opening a duplicate. For bug reports, include your NetBird version, operating system, deployment type (Cloud, self-hosted, Kubernetes, or Docker), reproduction steps, expected and actual

behavior, and a debug bundle where relevant: uploads the bundle and prints a file key you can paste instead of attaching the archive. anonymizes the output, which matters on a public thread. It masks most identifying details but is not full redaction, so read the bundle before posting it. IPv4 private, CGNAT, and link-local ranges are kept | | | (implies ) | The above, plus IPv4 private, CGNAT, and link-local ranges, peer names in front of , , and , and WireGuard public keys. Labels

under are kept, since it only hosts infrastructure | See collecting a debug bundle and the CLI reference for details. See

Frequently asked questions

How many stars and forks are recorded?

netbirdio/netbird has 30,012 stars and 1,760 forks.

What is the repository rank?

netbirdio/netbird is ranked 512.

What language and category are recorded?

netbirdio/netbird has 30,012 stars, uses Go and belongs to Infrastructure.

Which repository is closest in rank?

netbirdio/netbird is compared with FlashML-org/FreeVideo, ranked 503 with 1,993 stars.

README
 ![NetBird logo](docs/media/logo-full.png) 


[![SonarCloud alert status](https://sonarcloud.io/api/project_badges/measure?project=netbirdio_netbird&metric=alert_status)](https://sonarcloud.io/dashboard?id=netbirdio_netbird)
[![BSD-3 License](https://img.shields.io/badge/license-BSD--3-blue)](https://github.com/netbirdio/netbird/blob/main/LICENSE)
[![NetBird Slack](https://img.shields.io/badge/slack-@netbird-red.svg?logo=slack)](https://docs.netbird.io/slack-url)
[![Community forum](https://img.shields.io/badge/community%20forum-@netbird-red.svg?logo=discourse)](https://forum.netbird.io)
[![Gurubase: Ask NetBird Guru](https://img.shields.io/badge/Gurubase-Ask%20NetBird%20Guru-006BFF)](https://gurubase.io/g/netbird)


Start using NetBird at [netbird.io](https://netbird.io/pricing)
  

See [Documentation](https://docs.netbird.io/)
  

Join our [Slack channel](https://docs.netbird.io/slack-url) or our [Community forum](https://forum.netbird.io)


🚀 [We are hiring! Join us at https://netbird.io/careers](https://netbird.io/careers)

🤖 NetBird Agent Network (Beta)

Identity-aware access control for AI agents — keyless access to LLM APIs and private resources over the encrypted NetBird tunnel. See agent-network/ or read the docs at netbird.ai.

NetBird combines a configuration-free peer-to-peer private network and a centralized access control system in a single platform, making it easy to create secure private networks for your organization or home.

Connect. NetBird creates a WireGuard-based overlay network that automatically connects your machines over an encrypted tunnel, leaving behind the hassle of opening ports, complex firewall rules, VPN gateways, and so forth.

Secure. NetBird enables secure remote access by applying granular access policies while allowing you to manage them intuitively from a single place. Works universally on any infrastructure.

https://github.com/user-attachments/assets/10cec749-bb56-4ab3-97af-4e38850108d2

Self-host NetBird (video)
Key features

Connectivity Management Security Automation Platforms
✓ Kernel WireGuard ✓ Admin Web UI ✓ SSO & MFA support ✓ Public API ✓ Linux
✓ Peer-to-peer connections ✓ Auto peer discovery and configuration ✓ Access control: groups & rules ✓ Setup keys for bulk provisioning ✓ macOS
✓ Connection relay fallback ✓ IdP integrations ✓ Activity logging ✓ Self-hosting quickstart script ✓ Windows
✓ Routes to external networks ✓ Private DNS ✓ Traffic events ✓ IdP groups sync with JWT ✓ Android
✓ Domain-based DNS routes ✓ Custom DNS zones ✓ Device posture checks ✓ Terraform provider ✓ Android TV
✓ Exit nodes ✓ Multiuser support ✓ Peer-to-peer encryption ✓ Ansible collection ✓ iOS
✓ IPv6 dual-stack overlay ✓ Multi-account profile switching ✓ SSH with central access policies ✓ Apple TV
✓ Browser SSH & RDP ✓ Quantum-resistance with Rosenpass ✓ FreeBSD
✓ Reverse proxy with auto-TLS ✓ Periodic re-authentication ✓ pfSense
✓ OPNsense
✓ MikroTik RouterOS
✓ OpenWRT
✓ Synology
✓ TrueNAS
✓ Proxmox
✓ Raspberry Pi
✓ Serverless
✓ Container

Quickstart with NetBird Cloud

Quickstart with self-hosted NetBird

This is the quickest way to try self-hosted NetBird. It should take around 5 minutes to get started if you already have a public domain and a VM. Follow the Advanced guide with a custom identity provider for installations with different IdPs.

Infrastructure requirements:

  • A Linux VM with at least 1 CPU and 2 GB of memory.
  • The VM should be publicly accessible on TCP ports 80 and 443 and UDP port 3478.
  • A public domain name pointing to the VM.

Software requirements:

Steps

  • Download and run the installation script:
export NETBIRD_DOMAIN=netbird.example.com; curl -fsSL https://github.com/netbirdio/netbird/releases/latest/download/getting-started.sh | bash

A bit on NetBird internals

  • Every machine in the network runs the NetBird agent, which manages WireGuard.

  • Every agent connects to the Management Service, which holds network state, manages peer IPs, and distributes updates to agents.

  • Agents use ICE (via pion/ice) to discover connection candidates for peer-to-peer connections.

  • Candidates are discovered with the help of STUN servers.

  • Agents negotiate a connection through the Signal Service, exchanging end-to-end encrypted messages with candidates.

  • When NAT traversal fails (e.g. mobile carrier-grade NAT) and a direct p2p connection isn't possible, the system falls back to a Relay Service and a secure WireGuard tunnel is established through it.
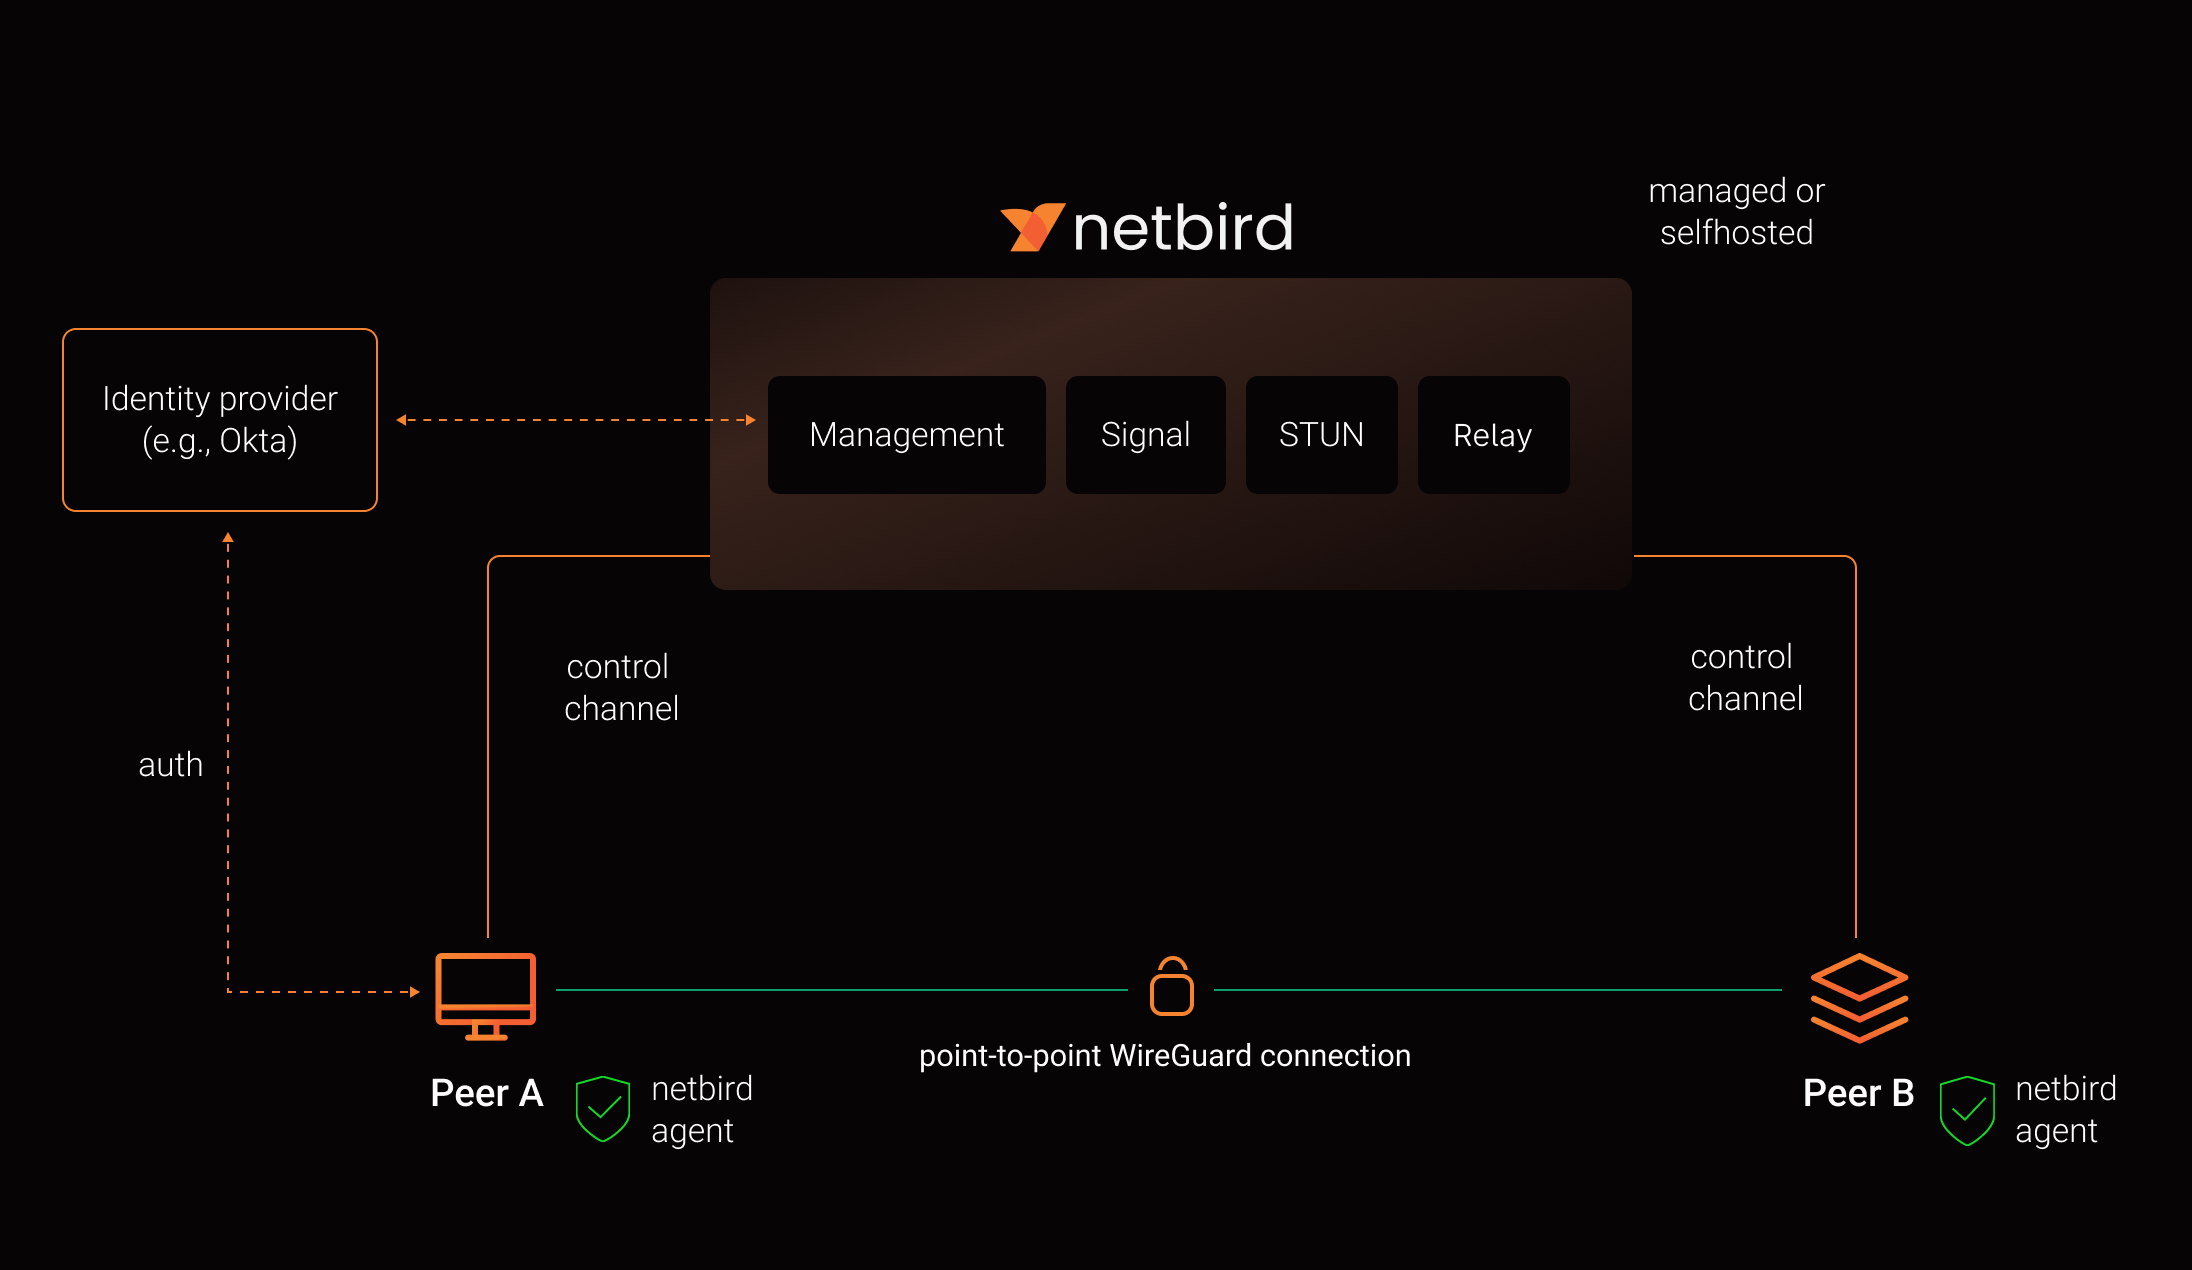
See a complete architecture overview for details.

Reporting bugs and requesting features

NetBird uses a discussion-first workflow. Bug reports and feature requests start in Discussions, not as issues.

What you want to do Where to go
Report a bug, regression, or unexpected behavior Issue Triage
Request a feature or share an idea Ideas & Feature Requests
Ask about setup, configuration, or self-hosting Q&A / Support
Report a security vulnerability Security policy, never a public thread

Our team and maintainers triage discussions, ask follow-up questions, check for duplicates, and reproduce bugs. Validated reports are promoted to issues. This keeps the issue tracker a clear answer to one question: what is the team working on.

Please search existing discussions and issues first, including closed ones. If something similar already exists, upvote it and add your details there instead of opening a duplicate.

For bug reports, include your NetBird version, operating system, deployment type (Cloud, self-hosted, Kubernetes, or Docker), reproduction steps, expected and actual behavior, and a debug bundle where relevant:

netbird version
netbird status -d -A
netbird debug for 1m -A -S -U

-U uploads the bundle and prints a file key you can paste instead of attaching the archive. -A anonymizes the output, which matters on a public thread. It masks most identifying details but is not full redaction, so read the bundle before posting it. Two levels are available:

Level How to select What it masks
default -A / --anonymize Public IP addresses, IPv6 ULA addresses, MAC addresses, and domains other than netbird.io, netbird.cloud, netbird.selfhosted, and netbird.stage. IPv4 private, CGNAT, and link-local ranges are kept
strict --anonymize-level strict (implies -A) The above, plus IPv4 private, CGNAT, and link-local ranges, peer names in front of netbird.cloud, netbird.selfhosted, and netbird.stage, and WireGuard public keys. Labels under netbird.io are kept, since it only hosts infrastructure

See collecting a debug bundle and the CLI reference for details.

See How to use Discussions, Issues, and Pull Requests for the full workflow, or SUPPORT.md for a shorter version.

Contributing

Contributions are welcome. Read CONTRIBUTING.md first. NetBird works ticket first, anything that changes behavior needs an issue the team has agreed on before you open a pull request.

Community projects

Note: The main branch may be in an unstable or even broken state during development. For stable versions, see releases.

Support acknowledgement

In November 2022, NetBird joined the StartUpSecure program sponsored by the Federal Ministry of Education and Research of the Federal Republic of Germany. Together with the CISPA Helmholtz Center for Information Security, NetBird brings security best practices and simplicity to private networking.
Acknowledgements

We build on open source technologies like WireGuard®, Pion ICE, and Rosenpass. We greatly appreciate the work these projects are doing, and we'd love it if you could support them too (e.g., by starring or contributing).

Legal

This repository is licensed under the BSD-3-Clause license, which applies to all parts of the repository except for the directories management/, signal/ and relay/. Those directories are licensed under the GNU Affero General Public License version 3.0 (AGPLv3). See the respective LICENSE files inside each directory.

WireGuard and the WireGuard logo are registered trademarks of Jason A. Donenfeld.

Nearby in the ranking
Similar items