Give your AI a real, persistent memory. The open-source system plus templates that turn an Obsidian vault into your AI's working memory. No vector database, just markdown.
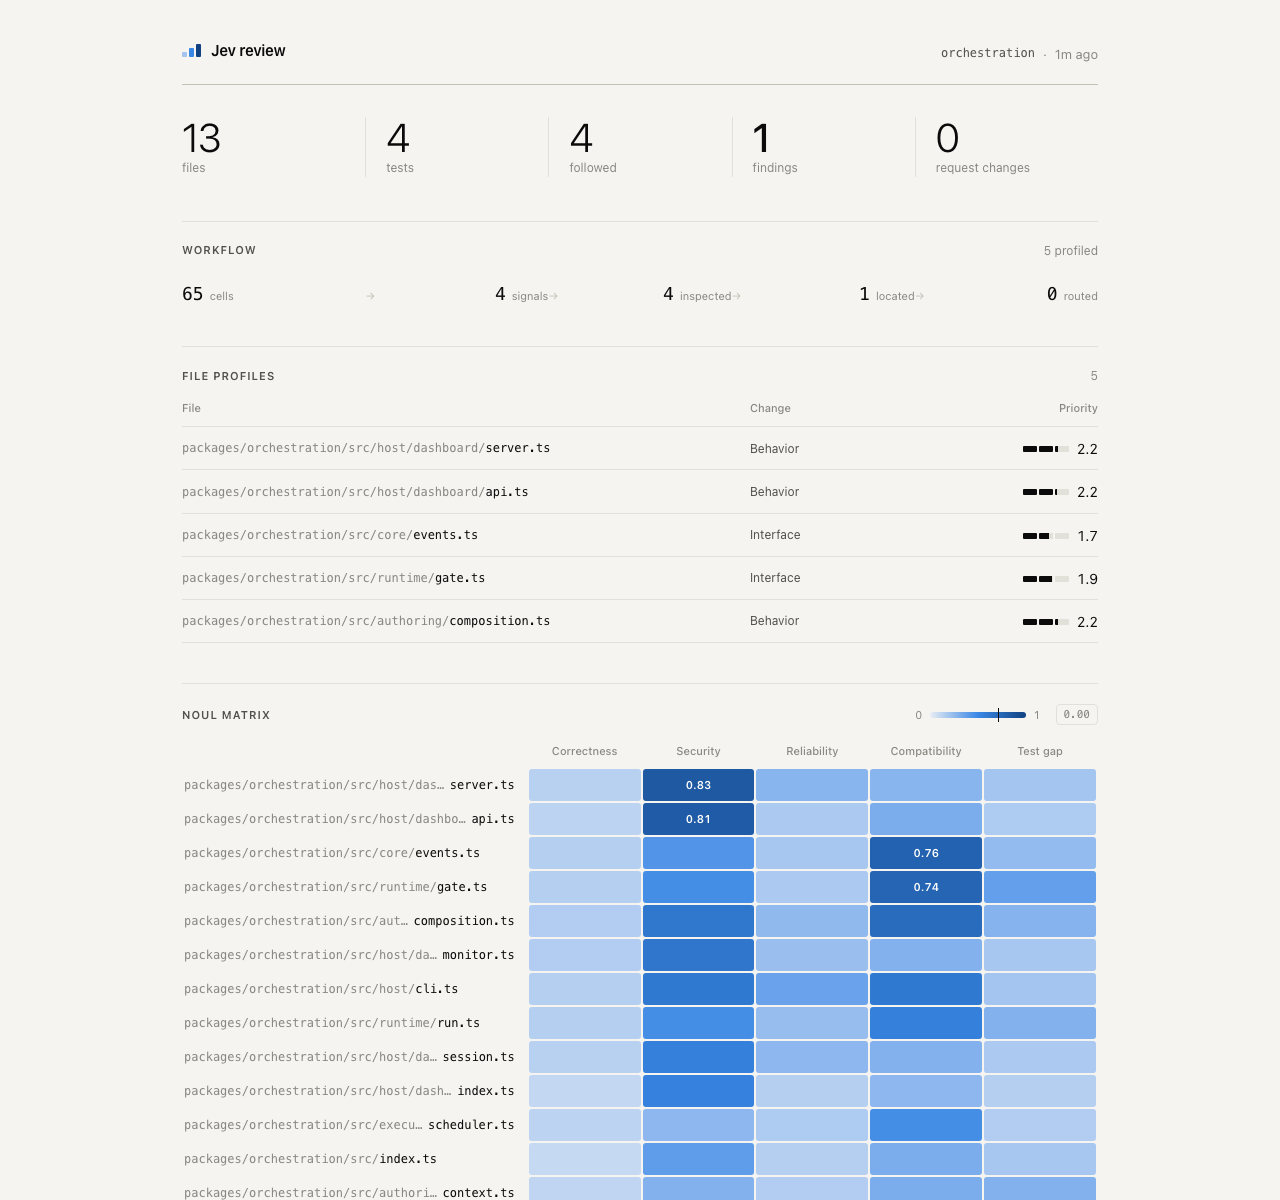
Jev Review A small code-review workflow built with TypeSafe Jev. It can review a Git diff or scan a complete codebase, follows the strongest structured signals through focused model calls, and presents the result in a quiet local dashboard. How It Works The reviewer keeps orchestration in code and uses Jev for bounded judgments: Exposes separate change-review and complete-codebase entry points. Uses changed or related tests as context when judging test gaps. Screens correctness, security, reliability, compatibility
, and test coverage. Selects concrete diff hunks or source regions before scoring impact. Uses structured hints, counterexamples, and explicit decision boundaries. Applies thresholds and workflow policy in code. Shows large reports in collapsible dashboard sections. Binds the dashboard to and never serves environment files. Current Scope This is an experiment in composing fast typed judgments into a review workflow. It does not yet integrate compiler diagnostics, static analyzers, repository indexing, or generated explanations. Findings are review prompts, not proof of
a defect.
Frequently asked questions
How many stars and forks are recorded?
devagrawal09/jev-review has 688 stars and 45 forks.
What is the repository rank?
devagrawal09/jev-review is ranked 4,176.
What language and category are recorded?
devagrawal09/jev-review has 688 stars, uses TypeScript and belongs to AI Engineering.
Which repository is closest in rank?
devagrawal09/jev-review is compared with buzzer-re/Rikugan, ranked 4,175 with 689 stars.
README
Jev Review
A small code-review workflow built with TypeSafe Jev. It can review a Git diff or scan a complete codebase, follows the strongest structured signals through focused model calls, and presents the result in a quiet local dashboard.
How It Works
The reviewer keeps orchestration in code and uses Jev for bounded judgments:
npm install
cp .env.example .env
# Add TYPESAFE_API_KEY to .env

# Review the current Git diff
npm run review:changes:save -- /path/to/git/repository

# Or scan every non-ignored source file under a scope
npm run review:codebase:save -- /path/to/git/repository-or-package
npm run dashboard
scripts/check-dependencies.ts fails npm run check on any upward import, any
import between cli and dashboard, or any cycle.
Current Scope
This is an experiment in composing fast typed judgments into a review workflow. It does not yet integrate compiler diagnostics, static analyzers, repository indexing, or generated explanations. Findings are review prompts, not proof of a defect.